Access Enriched IOC Data In Real-Time To Proactively Prevent Threats
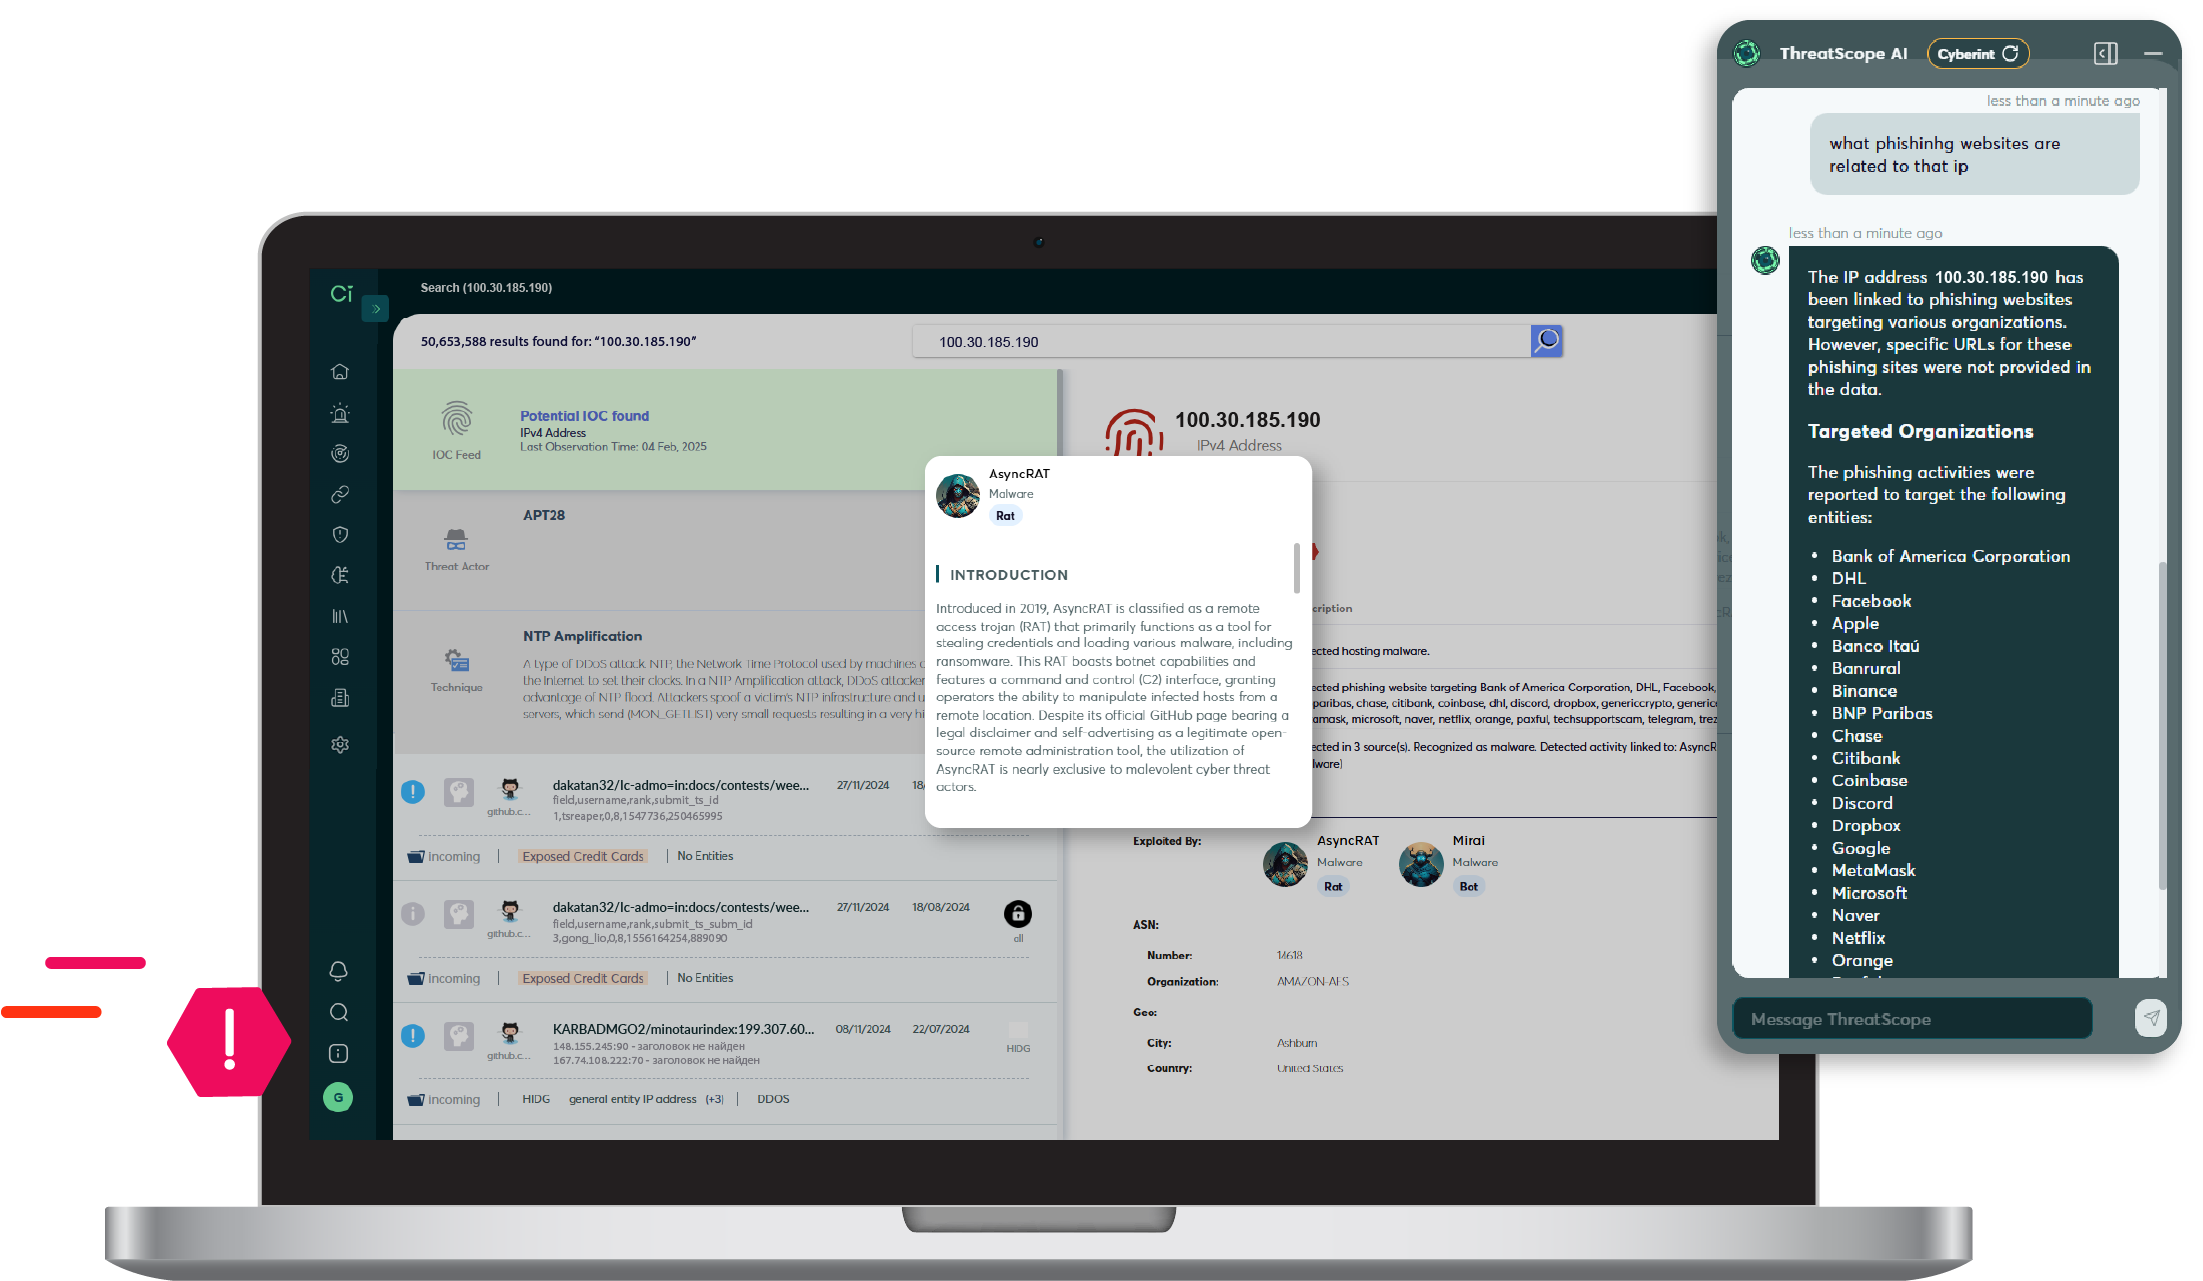
Gain access to enriched, global threat data collected from Check Point’s global network of firewalls and gateways, combined with Cyberint’s proprietary intelligence and best-in-class OSINT feeds.
60
M
New intelligence items/month
1.7
M
malicious indicators identified each day
3.7
B
websites and files inspected daily
Unparalleled Visibility On Active Threats
Superior Threat Data, Delivered In Real Time
The IOC Data You Need To Stay Secure
Supercharge Your Security Stack
Leverage Cyberint’s Risk Intelligence data to get more out of existing security investments, including SIEM, SOAR, XDR, and other products.
Elevate Your Threat Hunting Program
Threat Hunters can access real-time data on any IOC through Cyberint’s Google Chrome browser extension or through Forensic Canvas, an advanced investigations tool.
Access Enriched IOCs In Multiple Formats
Cyberint provides data on malicious IP addresses, domains, URLs, and file hashes. Each IOC is enriched with threat type, description, date of observation, confidence level, region, and more.
Choose How You Consume Data
Ingest Cyberint’s Risk Intelligence data in the form of daily IOC feed or via a RESTful IOC enrichment API that provides data upon request and can be used for custom integrations.
Prevent outbound communication with known C2 servers.
Botnets
Prevent Botnet based attacks, such as credential stuffing and DDoS.
Infected machines
Continuously correlate your IP addresses with those found in malware logs.
Anonymization
Detect traffic to or from TOR exit nodes and your corporate network.
Phishing
Prevent communication with phishing domains, URLs, and IP addresses.
Malware payloads
Detect malicious file hashes and generate alerts when one is found.
OUR ADVANTAGE
Why Customers Choose Argos
Detect malicious file hashes and generate alerts when one is found.
Cyberint, a Check Point company, has greater breadth and depth of IOC data collection, all distributed to customers in real time.
Fully Enriched Malicious Indicators
Every IOC is fully enriched, giving your team the context they need to understand the threat and what actions should be taken.
Flexible Ingestion & Consumption of IOCs
Use Cyberint’s Risk Intelligence data in multiple ways, including a daily feed, an IOC enrichment API, a Chrome browser extension, and an investigations tool.
Detect malicious file hashes and generate alerts when one is found.
Cyberint, a Check Point company, has greater breadth and depth of IOC data collection, all distributed to customers in real time.
Fully Enriched Malicious Indicators
Every IOC is fully enriched, giving your team the context they need to understand the threat and what actions should be taken.
Flexible Ingestion & Consumption of IOCs
Use Cyberint’s Risk Intelligence data in multiple ways, including a daily feed, an IOC enrichment API, a Chrome browser extension, and an investigations tool.
Testimonials
24/7,
« La solution Cyberint de Threat Intelligence ciblées est une plateforme conviviale qui fournit 24 heures sur 24 et 7 jours sur 7 des alertes en temps quasi réel provenant du web ouvert, du web profond et du dark web ».