


The Cyberint Research Team work round the clock to unearth the latest threats to SMBs and enterprises. They are on top of the latest TTPs and monitor rising threat groups, malwares and trends.
This report profiles n0n, a financially motivated data-theft extortion group that emerged in September 2026. It examines the group’s activity, victimology, tactics, techniques, and procedures (TTPs), extortion practices, and potential risks to organizations.
As of October 19, 2026, the largest public tracker reviewed recorded 120 listed victims across 28 countries, reflecting rapid growth since the group’s emergence. Notably, on October 12, n0n listed 38 organizations across the global maritime and logistics sectors in a single wave, spanning 18 countries. Although stolen credentials associated with infostealer malware appear to be an important initial access method, analysis of the maritime campaign suggests that the 38 listings may originate from exposure through a shared application or vulnerability rather than independent network intrusions. This hypothesis is supported by similarities in the claimed datasets, their relatively limited size, and the absence of identified infostealer credential matches for many affected organizations. Overall Assessment: n0n represents an emerging extortion threat characterized by rapid expansion of its public victim list, opportunistic targeting, and potential exploitation of shared technology infrastructure. Organizations with exposed credentials, insufficiently secured remote access, or dependencies on third-party service providers may face increased exposure.
Most reported compromises and data-theft claims remain independently unverified. Organizations should prioritize credential security, external attack surface management, third-party risk assessment, and continuous monitoring for potential data exposure.
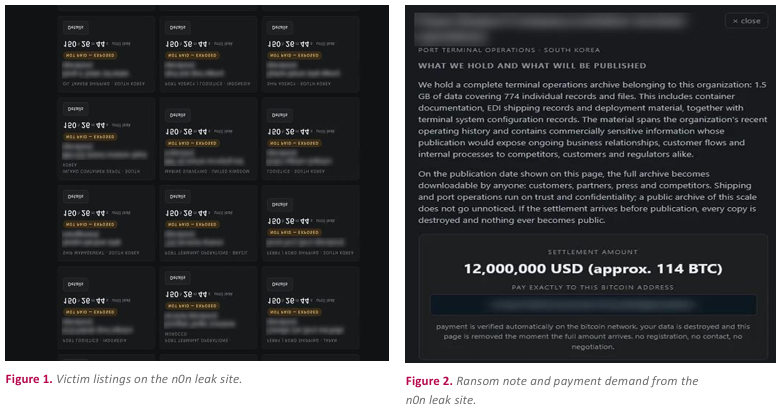
n0n (also written N0N) is a financially motivated extortion group first observed on September 18, 2026. No affiliation with other threat actors has been identified. The group operates as a data-theft extortion actor: it steals data and threatens to publish it unless the ransom is paid. No file encryption has been observed, and its leak-site listings refer only to stolen data. Observed ransom demands range from $2.4 million to $25 million. n0n does not open a communication channel with its victims. Instead, it publishes an individual ransom note for each victim on its Tor-based data leak site, alongside a countdown to the publication of the stolen data.
| Alias | n0n, N0N |
| Affiliations | unknown |
| Communication | No Communication |
| Activity History | September 18, 2026 |
| Threat Type | Data-theft extortion (no encryption observed) |
| Extortion Strategy | Single extortion (threat to leak stolen data) |
| Extortion Amounts | 2,400,000$-25,000,000$ |
| Ransom Note Name | The ransom note is published on the site and varies from victim to victim. |
| Data Leak Sites | nongzecboljwv3yfndkggsybsglfrkffw7bvk2zemuteoxe6etpusnad[.]onion |
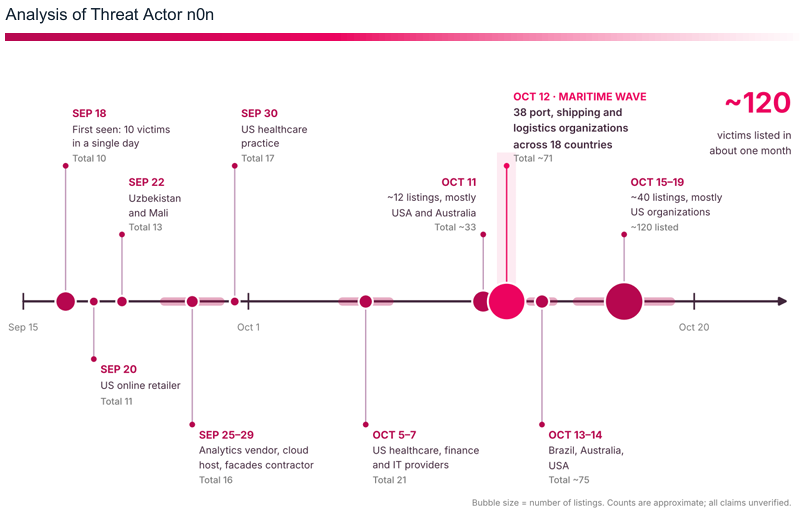
n0n has moved fast. In about one month of activity, it has listed roughly 120 victims on its leak site. The group posted 10 victims on its first day, September 18, and fewer than 20 by the end of September. In October the pace accelerated sharply, with listings arriving in large waves: about a dozen on October 11, 38 maritime and logistics organizations on October 12, and about 40 more between October 15 and 19. Payment deadlines of one to seven days add pressure on victims and leave little time to respond.
Deadlines in the listings we reviewed run from one to seven days. A cloud hosting provider received three days, listings on October 5 had one to two days, and the October 12 port listings had seven. All data below is claimed by the actor and unverified.
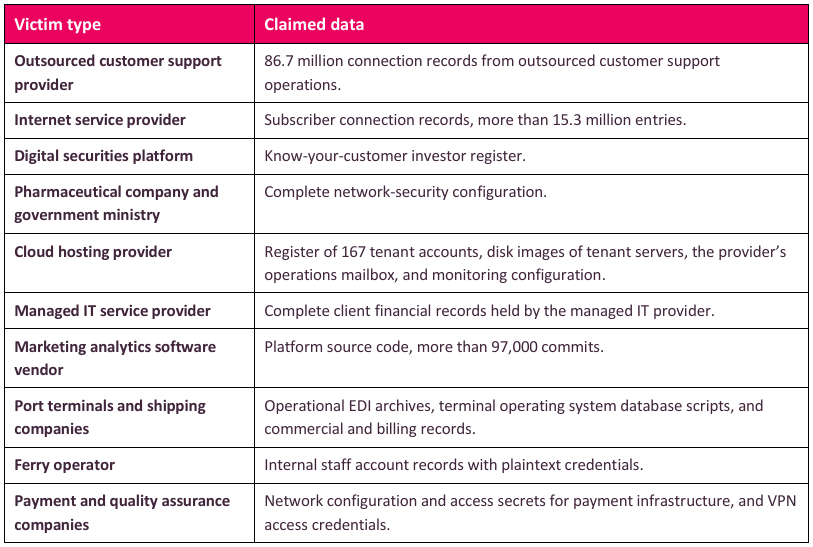
Many listings claim operational and configuration data, such as network-security configurations, Active Directory mappings, database scripts, and credentials, not only customer records. That material can support follow-on intrusion. This is our reading of the listings, not a claim by the group.
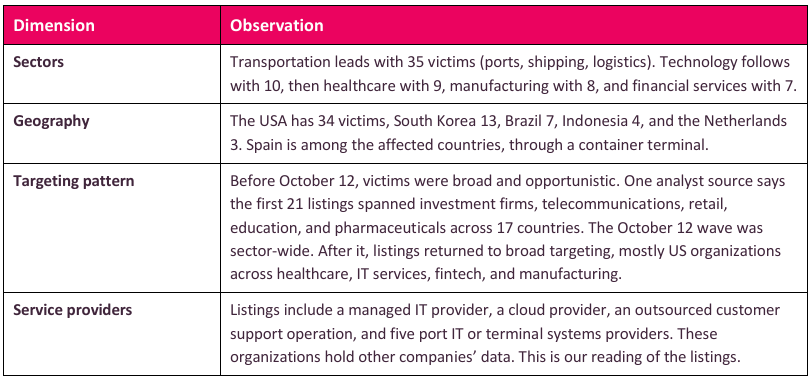
Insights: n0n’s victim list is wide rather than deep. Transportation tops the sector count almost entirely because of the single October 12 wave. Outside that wave, the group hits whatever it can reach, across healthcare, technology, manufacturing and financial services. The same wave explains South Korea’s second place behind the USA, since many of the listed maritime firms are Korean. The most consequential pattern is the share of service providers among the victims: managed IT, cloud, customer support and port IT firms hold other companies’ data, so a single listing can expose many downstream organizations.
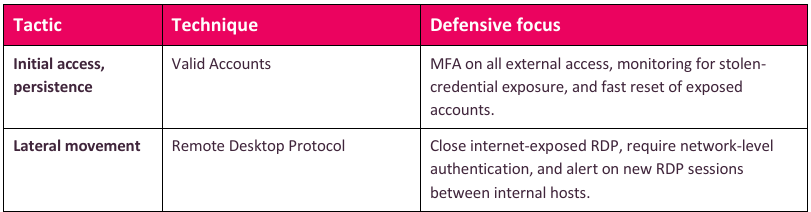
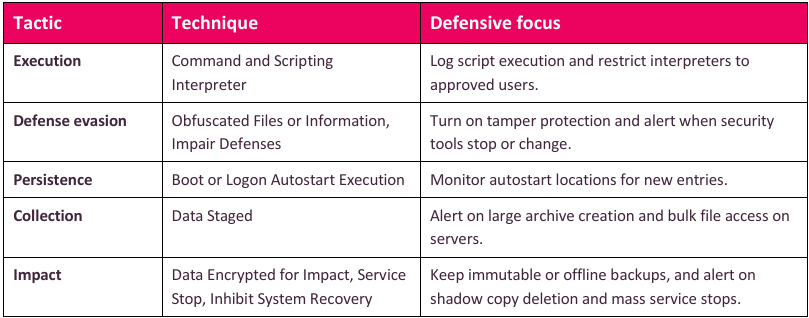
The table maps techniques that associated to n0n to the defensive focus we recommend.
Based on n0n’s reported access method and victim list, we assess that the following types of organizations are the most likely targets:
This assessment rests on tracker data and public research. Because most listings are unverified actor claims, we rate our confidence as moderate.
Check Point’s exposure management changes the game.
We combine billions of internal telemetry points with billions of external signals from the open, deep, and dark web to deliver a unified intelligence fabric. This provides clear visibility across the full attack surface, including brand risk.
The industry is moving from fragmented feeds to real context and real priorities. We support that shift through active threat validation, confirmation of compensating controls, and deduplication across tools, so teams can focus on what actually matters.
With safe-by-design remediation, fixes aren’t just assigned, they’re implemented. Every fix is validated before enforcement, enabling measurable risk reduction without downtime.
Gartner predicts organizations adopting continuous threat exposure management with mobilization will see 50% fewer successful attacks by 2028. We’re leading that shift with action, not just tickets, and Fortune 500 organizations across major industries already rely on Check Point Exposure Management.
For more information visit: https://www.checkpoint.com/exposure-management/