

Deep & Dark Web Monitoring
Collect and analyze millions of elusive deep and dark web sources others miss to identify leaked credentials, brand mentions, PII, malware activity, and emerging threats. Virtual HUMINT, powerful AI engines, and expert analysts actively engage threat actor communities.

See Deep & Dark Web Monitoring in Action
Level Up Your Deep & Dark Web Monitoring
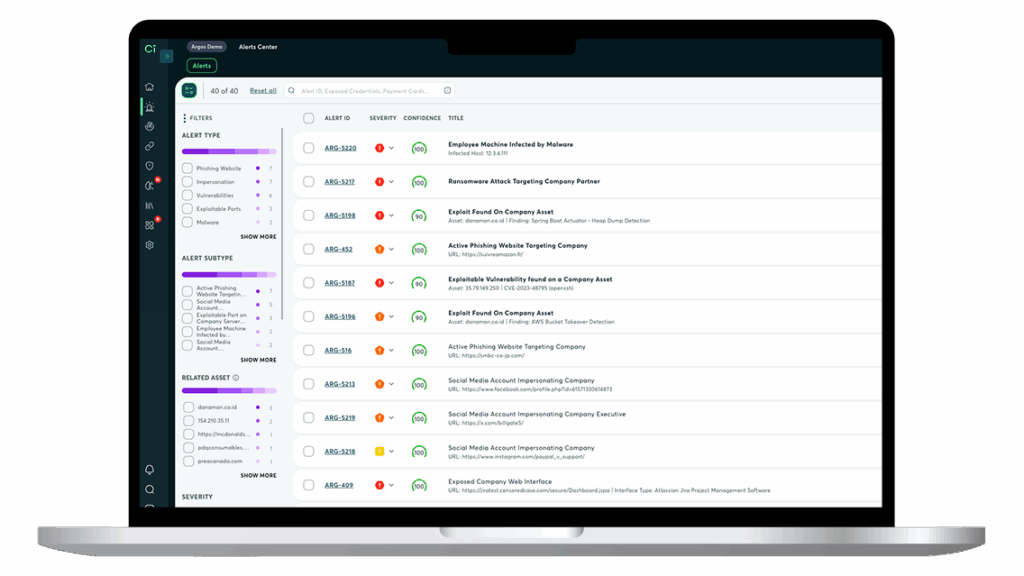
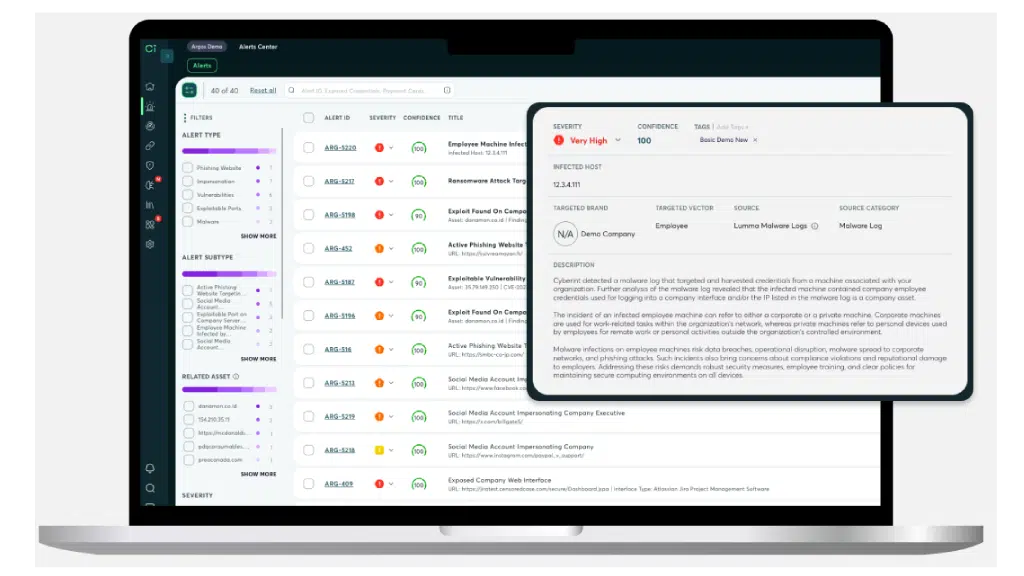
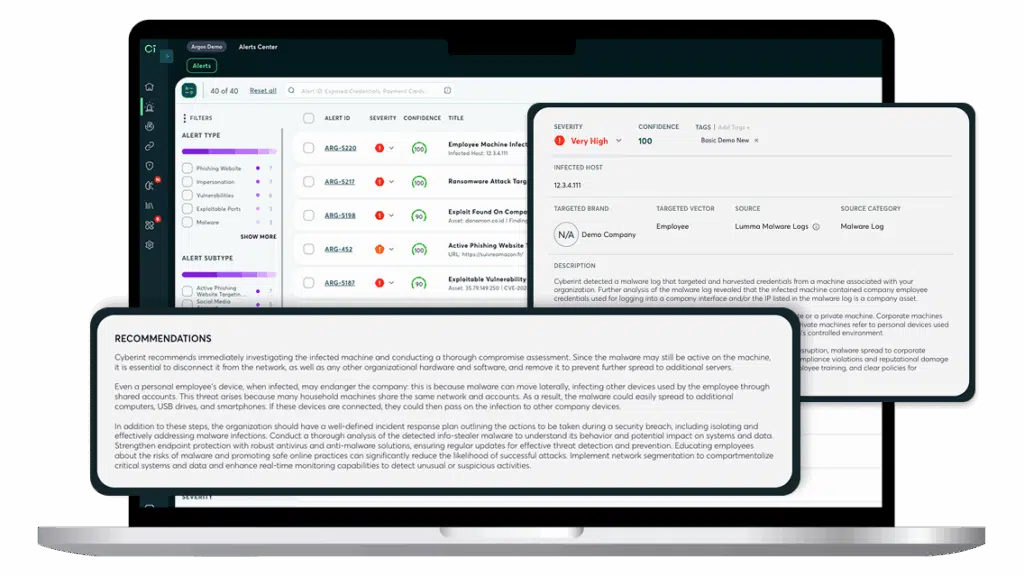
The Power of Dark Web Hunting
Investigate threats connected to your organization through dark web threat hunting and actionable dark web intelligence. Explore threat actors, targeted attacks, TTPs, and relationships between indicators to uncover risks across hard to reach sources.
How it works
Uncover known and unknown assets and access points

Bypass the protective layer

Identify Leaked Data

Determine the Source

Prioritize for Highest Impact
We have a really good relationship with customer support and the analyst teams.” Said Evans, “We are constantly being alerted about things to respond to. Because we’re a small team they are like an extension of us – which really helps from a risk management standpoint.
Evans Duvall, Cyber Security Engineer at Terex
In the POV we realized that Exposure Management was much more than an EASM solution, it delivered much value with highly relevant intelligence from the deep and dark web.
Benjamin Bachmann, Head of Group Information Security Office at Ströer
We looked at some other vendors and they have good solutions, but we needed more than what they could offer. With Exposure Management, I can continuously monitor not only all of Phoenix Petroleum’s domains, but all our digital assets, plus we get relevant intelligence from the deep and dark web.
Roland Villavieja, Information Security Officer at Phoenix Petroleum
We were looking to establish a new threat intelligence capability within Questrade and, in order to support that, we needed to have a platform that would give us deep insights.
With Infinity ERM, we’re not only getting intelligence from the general landscape but we’re also getting intelligence that’s really tailored to us and our environment.
Shira Schneidman, Cyber Threat & Vulnerability Senior Manager at Questrade
Once we identified the need to address the risk of fraudulent websites and social profiles, I quickly realized we needed to handle this in a scalable manner. Our solution is to use Exposure Management to help us automatically detect and takedown these threats.
Ken Lee, IT Risk and Governance Manager at WeBull
Resources


Find Your Exposed Data Before Threat Actors Do
See how we use deep and dark web monitoring to uncover compromised credentials, exposed data, and threats targeting your organization.
Start With a DemoFAQs
How intrusive is Check Point’s external discovery process? When you scan is there any active testing?
Check Point Exposure Management continuously discovers the open, deep and dark web to detect all of the external IT assets in a customer’s digital footprint. The process is fully automated and passive so it does not actively validate or test any security controls. The discovery process will not “set off any alarm bells” or give security teams the impression an attack is underway. There is no impact on normal operations.
There is an optional additional feature named agentic exploitability validation, which we detail below that does actively validate.
Using publicly-available data, like DNS records, WHOIS data, and SSL certificates, Cyberint’s Attack Surface Management module is able to map out an organization’s external attack surface. All discovered assets are checked for common security issues. The categories of assets detected are: IP addresses, domains, subdomains, cloud storage, and organizations (i.e. trademarked brands).
These are the types of security issues we identify:
- Certificate Authority issues
- Compromised Credentials
- Email Security issues
- Exploitable Ports
- Exposed Cloud Storage
- Exposed Web Interfaces
- Hijackable Subdomains
- Mail Servers In Blocklist
- SSL/TLS issues
About Agentic Exploitabilitiy Validation (AEV): Check Point’s AEV capability goes beyond typical CVE detection to actively test for exploitability. AEV also performs other automated tests to uncover common security issues in your organization’s digital assets that fall outside the scope of a vulnerability database. Alerts are issued in real time so you can quickly identify and remediate your most urgent risks. AEV enables the crucial validation step to be tackled in the CTEM framework.
My company has many different brands, can I monitor them individually?
Yes, as our platform is multi-tenant, we can set up an Attack Surface Management (ASM) instance for each brand and monitor the brands separately.
Can you automate actions based on alerts and integrate with other tools?
Yes. All alerts can be automatically sent to SIEM/SOAR platforms to trigger automated playbooks. We have an API that can integrate our information into existing SIEM/SOAR solutions and corelate with information from other intelligence platforms. We also integrate with Splunk, Azure AD, AWS, JIRA, OKTA, Qradar, XSOAR out of the box.
We know also have a Threat Intelligence Platform that combines and prioritizes different threat intel feeds and sends to SIEM/SOAR solutions to remediate.
What sources do you cover?
We cover thousands of sources from the clear, deep, and dark web. We cover:
- Search engines such as Bing and Google
- All the major cybercrime forums such as Breach Forums etc.
- Instant messaging platforms such as Telegram & Discord
- Social media
- Blogs
- GitHub and other pastesites
- Application stores
- File sharing websites
- Security Feeds
- Data leakage sites
- Credit Card stores
- Blackmarkets such as RussianMarket and 2easy.shop
- Malware logs
- Dark networks
and more. 5% of our sources are considered “Dark web”. The rest are in the clear/deep web.
How often do you crawl and scrape your sources? And how do you evade detection?
Each source is crawled and scraped according to the allowed policies on it. For example, if a dark web forum is monitored for suspicious scraping activity, we will make sure we collect information at a pace that does not raise any suspicion. We try to keep each source up to date with no longer than a week between each scraping (often much much more).
How do you deal with language barriers?
We have automated translation mechanisms in place and our the Check Point Exposure Management team speaks over 22 languages fluently, including Russian, Arabic, English, Chinese, Japanese, Filipino languages like Tagalog, Ilocano and Ilonggo and more.
Can you add new sources on demand?
Our sources team is constantly looking for and adding more sources. Every request is examined by the team and we are more than happy to add additional sources that can provide value to our customers. The turn-around time for adding a source is relatively short (1-4 weeks usually).
Do you create generic threat reports?
Check Point has a very experienced research team that tracks global threat events and releases periodic research reports. Every major global event that occurs is covered by the Check Point Exposure Management/Check Point research team. For example, we have published reports on: the 2026 Iran War, Scattered Spider, The Russian-Ukraine war, the Log4shell vulnerability, specific Ransomware groups tracking and more.
Do you create dedicated reports for my company?
Our research team can create reports on any desired subject, using “investigation hours”. Each customer can purchase these hours and each research is priced based on the number of hours required to complete it. The subjects vary between VIP exposure reports, industry related threats, Incident response, Deep investigations and more


